When Should a Program Escalate a Risk? Program Risk Escalation Criteria
TL;DR
We explain that a program risk should be escalated when its consequences exceed the current owner’s authority or capacity to respond. Our PgMP decision guide shows how to assign ownership, test tolerances and shared dependencies, connect risk to benefits and strategy, prepare evidence, and answer scenario questions without abandoning program-manager accountability.
For PgMP candidates, governance judgment is not peripheral, PMI’s current certification exam includes 170 questions that test how experienced practitioners think through program decisions.
Program risk escalation criteria are met when a risk’s consequences exceed the current owner’s authority or capacity to respond. Escalate when it threatens shared benefits, crosses component boundaries, breaches an agreed tolerance, jeopardizes strategic alignment, or requires an executive trade-off. The program manager still analyzes, coordinates, monitors, and reports the risk.
We will show how to assign risk ownership, apply four escalation tests, build decision-ready evidence, and answer PgMP-style scenarios without treating escalation as a way to abandon accountability.
When Do Program Risk Escalation Criteria Trigger Action?
Most teams escalate risks too late because they confuse visibility with authority. A risk can be highly visible, serious, and still manageable by the project or component owner. Conversely, a moderately rated risk can demand immediate escalation when it affects a shared dependency or requires someone to approve a decision outside the program manager’s mandate.
Escalation is a response to an ownership gap. The current PMI lexicon defines it as transferring ownership to a relevant party when a risk sits outside the team’s scope or authority. In practice, the program manager should retain responsibility for making the decision intelligible, coordinating the response, and tracking what changes after the handoff.
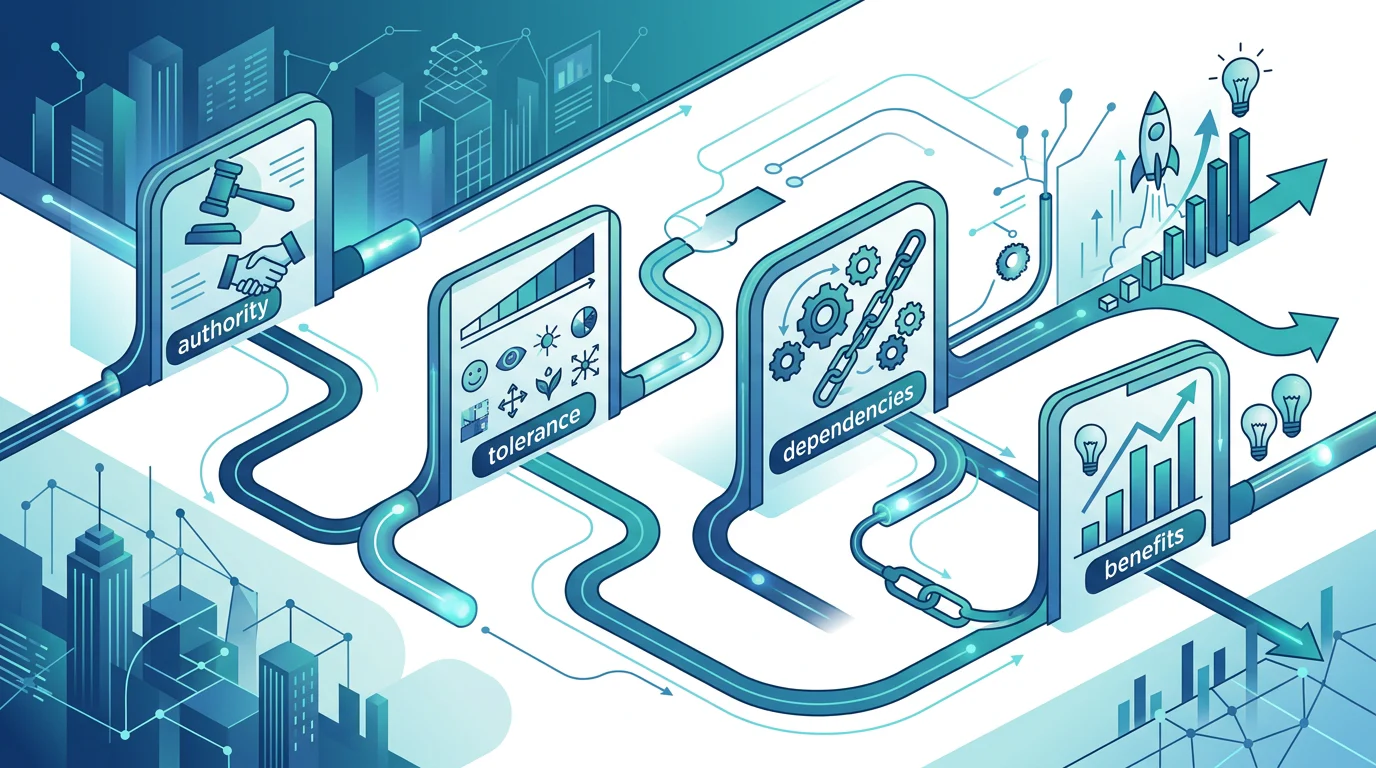
Use the criteria as a sequence of questions:
- Authority: Can the current owner approve the necessary funding, policy exception, resource shift, or scope trade-off?
- Tolerance: Is the risk beyond an approved schedule, cost, compliance, benefit, or exposure limit?
- Dependency: Does it affect more than one component, a shared supplier, a platform, or a common release sequence?
- Value: Does it threaten a benefit, strategic objective, or business-case assumption rather than a single deliverable?
We recommend practicing this distinction before memorizing terminology. Our exam-prep playbook helps candidates turn governance concepts into scenario-based decisions.
Who Owns Risk at Each Level?
Risk ownership should follow the level at which the needed decision can be made. That is why program risk is not merely a larger project risk. A program exists to coordinate related work for benefits that individual projects could not obtain alone, so its risks often involve relationships, outcomes, and decisions that no component owner can resolve independently.
| Risk Level | Primary Impact | Typical Decision Owner | Escalate When |
|---|---|---|---|
| Project | One project’s scope, deliverables, budget, or schedule | Project manager | Local authority or contingency is insufficient |
| Component | One subprogram, operational activity, or project cluster | Component owner | The response affects another component or exceeds delegated limits |
| Program | Shared dependencies, benefits, sequencing, or common resources | Program manager | A sponsor or enterprise decision is required |
| Enterprise | Strategy, appetite, policy, investment, or business case | Sponsor, steering group, or executive governance | The response changes organizational direction or commitment |
Project and Component Ownership
Keep a risk at project or component level when its cause, consequence, and response remain local. For example, a team may resolve a test-environment delay inside approved contingency without changing another component’s delivery date or benefit forecast. Escalating every concern weakens governance because decision-makers receive noise rather than requests that need their authority.
A project manager should still report changing conditions upward. Candidates documenting program experience can use application domains to distinguish local delivery control from evidence of program-level coordination.
Program Ownership
A risk becomes a program concern when the response requires balancing component needs to protect a shared outcome. The program manager can resequence work, coordinate dependency owners, recommend resource allocation, and update benefit forecasts within the program’s governance boundaries.
This is especially important in cross-functional work, where influence may exceed formal control. Program leaders must clarify who can decide, not simply who is affected.
Enterprise Ownership
Enterprise escalation is appropriate when the risk challenges strategy, risk appetite, policy, investment priority, or the continuing validity of the business case. Senior governance may delegate work back down, but it must own the trade-off if it changes what the organization is willing to accept.
How Do the Four Escalation Tests Work?
The four tests work best in order. Start with authority, then test tolerance, dependency, and value. A risk that fails only one test may still need escalation, but passing all four strongly indicates that it belongs at a higher governance level.
Does the Response Exceed Current Authority?
Ask what action would actually reduce the exposure. If the answer involves transferring funds, accepting a regulatory exception, changing a policy, prioritizing one benefit over another, or directing a shared executive resource, the owner may lack authority even if they understand the risk perfectly.
Escalation should name that gap precisely. “Needs sponsor approval to release contingency” is stronger than “high risk, please advise” because it identifies both the required decision and the decision-maker.
Has a Tolerance Been Breached?
A risk register should not be a color-coded list detached from governance. Tolerances make escalation testable: a program might set limits for benefit variance, critical-path delay, residual exposure, regulatory impact, or consumption of management reserve.
The threshold must come from the organization’s governance model, not from a generic scorecard. Once a credible forecast shows breach, the program manager should escalate early enough for a real trade-off rather than waiting for an issue to become irreversible.
Does It Cross Component Boundaries?
Shared suppliers, platforms, resources, data, and milestones are common routes by which local risks become program risks. A supplier delay affecting one workstream may be manageable. The same delay affecting three release-dependent components can alter the entire benefits timeline.
Use a dependency map before aggregating ratings. Program-level risk research emphasizes reassessing escalated and aggregated risks against program thresholds, rather than simply adding project scores. That approach matches the strategic logic behind a strategic alignment framework.
Does It Threaten Benefits or Strategy?
A component can meet its delivery target while the program misses its intended value. That is why benefit exposure is often the decisive escalation test. PMI’s PgMP content outline expects candidates to analyze benefits plans for uncertainty, risk, mitigation, and corrective action.
For a scenario answer, connect the risk to a measurable benefit, then state who can protect it. This is the same governance logic candidates use when they map program decisions to the certification process.
What Evidence Makes an Escalation Decision Ready?
A sponsor cannot make a sound decision from a risk title and a red status. We treat escalation as a compact decision packet: it should describe the uncertainty, quantify the credible consequence where evidence permits, present options, and make the requested choice unmistakable.
The GAO schedule guide calls for prioritized risks and documented assumptions, methodology, data, and validated inputs in credible risk analysis. The same discipline applies to a program escalation, even when the risk concerns benefits, regulatory exposure, or adoption rather than schedule.
Candidates can connect this evidence to the governance expectations within the PgMP certification process, then explain why a specific decision must move to the next authority level.
Include these elements:
- Risk Statement: State the cause, uncertain event, and resulting consequence.
- Ownership Gap: Identify the current owner, proposed owner, and authority the current owner lacks.
- Exposure Trend: Show likelihood, impact, residual exposure, assumptions, and whether conditions are worsening.
- Dependency Evidence: List affected components, shared resources, or critical milestones.
- Benefit Effect: Name the benefit metric, forecast variance, and strategic objective at risk.
- Decision Request: Present feasible options, your recommendation, deadline, and consequence of delayed action.
- Follow-Through Plan: Specify response ownership, monitoring cadence, and the next governance review.
The program manager’s job does not end when a senior person accepts ownership. We expect the program manager to maintain the risk record, coordinate approved actions, update benefit forecasts, and re-escalate if residual exposure changes. Our application review support helps candidates test whether their documented reasoning has enough evidence to withstand review.
How Should PgMP Candidates Answer Risk Escalation Scenarios?
PgMP questions often include tempting details about urgency, stakeholder pressure, and local delivery problems. The best answer usually identifies the level of decision required before selecting an action. Do not escalate simply to display executive awareness, and do not keep a risk local when program value depends on coordinated action.
| Scenario | Correct Ownership Decision | Why |
|---|---|---|
| A shared identity platform delays three component releases and threatens the program’s adoption benefit | Escalate to program governance, then sponsor if funding, scope, or strategic trade-offs exceed program authority | The dependency and benefit exposure cross component boundaries |
| A test defect delays one component but remains inside approved contingency with no shared dependency | Keep it with the project or component owner, while monitoring defined triggers | The response remains within local authority and tolerance |
| A new regulation invalidates a business-case assumption across the organization | Elevate to enterprise governance | The response may change strategy, appetite, investment, or policy |
Use a Repeatable Scenario Answer
Work through every escalation scenario in five moves:
- Identify the current owner and the risk’s primary impact.
- Test whether authority or tolerance has been exceeded.
- Check for cross-component dependencies and benefit exposure.
- Name the next decision-maker and the evidence required.
- State how the program manager will coordinate and monitor after escalation.
This structure avoids two common errors: treating the sponsor as the default answer, and treating risk transfer as a release from responsibility. Use an exam readiness scorecard to find whether governance judgment, rather than recall, is the area that needs more practice.
Prepare PgMP Decisions with Augment Consultancy
At Augment Consultancy, we help experienced program leaders turn abstract standards into defensible decisions under exam pressure. Our PgMP preparation focuses on the judgment calls that separate component management from program leadership: benefit exposure, governance authority, stakeholder trade-offs, and evidence that explains why a particular action is next. We use scenario practice to make you classify the risk, name the rightful decision-maker, explain the escalation trigger, and retain accountability after the handoff. That same discipline supports stronger application narratives because it ties your decisions to strategy, benefits, and governance rather than vague responsibility claims. Before you sit the exam, our materials keep each answer anchored to the decision that protects program value. You can work through governance choices, benefit dependencies, and escalation rationale in a way that prepares you for realistic review conversations. Explore the complete learning path at Augment Consultancy Home
FAQs on Program Risk Escalation Criteria
These short answers reinforce the decision rule: escalate for authority, tolerance, dependency, or value exposure, then continue managing the risk after the handoff.
Does a High Risk Score Automatically Require Escalation?
No. A high score prompts analysis, but escalation depends on authority, tolerance, cross-component effects, benefit exposure, and whether another governance level must make the response decision.
When Does a Project Risk Become a Program Risk?
When its primary consequences or response cross component boundaries, threaten shared benefits, consume program-level contingency, or require coordination that the individual project manager cannot directly authorize.
Does Escalation Remove Program Manager Responsibility?
No. We expect the program manager to preserve the analysis, coordinate the approved response, monitor residual exposure, update benefits forecasts, and report progress to the new owner.
When Should a Program Risk Go to Enterprise Governance?
Escalate to enterprise governance when the response changes strategy, risk appetite, policy, investment priority, or business-case assumptions, rather than merely coordinating work already authorized within the program.